Before and after
        {{- if .Values.primary.initContainers }}
        {{- include "common.tplvalues.render" ( dict "value" .Values.primary.initContainers "context" $ ) | nindent 8 }}
        {{- end }}
      {{- end }}
      containers:
        - name: postgresql
          image: {{ include "postgresql.v1.image" . }}
          imagePullPolicy: {{ .Values.image.pullPolicy | quote }}
          {{- if .Values.primary.containerSecurityContext.enabled }}
          securityContext: {{- include "common.compatibility.renderSecurityContext" (dict "secContext" .Values.primary.containerSecurityContext "context" $) | nindent 12 }}
          {{- end }}
          {{- if .Values.diagnosticMode.enabled }}
          command: {{- include "common.tplvalues.render" (dict "value" .Values.diagnosticMode.command "context" $) | nindent 12 }}
          {{- else if .Values.primary.command }}
          command: {{- include "common.tplvalues.render" (dict "value" .Values.primary.command "context" $) | nindent 12 }}
          {{- end }}
16 lines of templates/primary/statefulset.yaml, around its image line. The chart has many files like this.
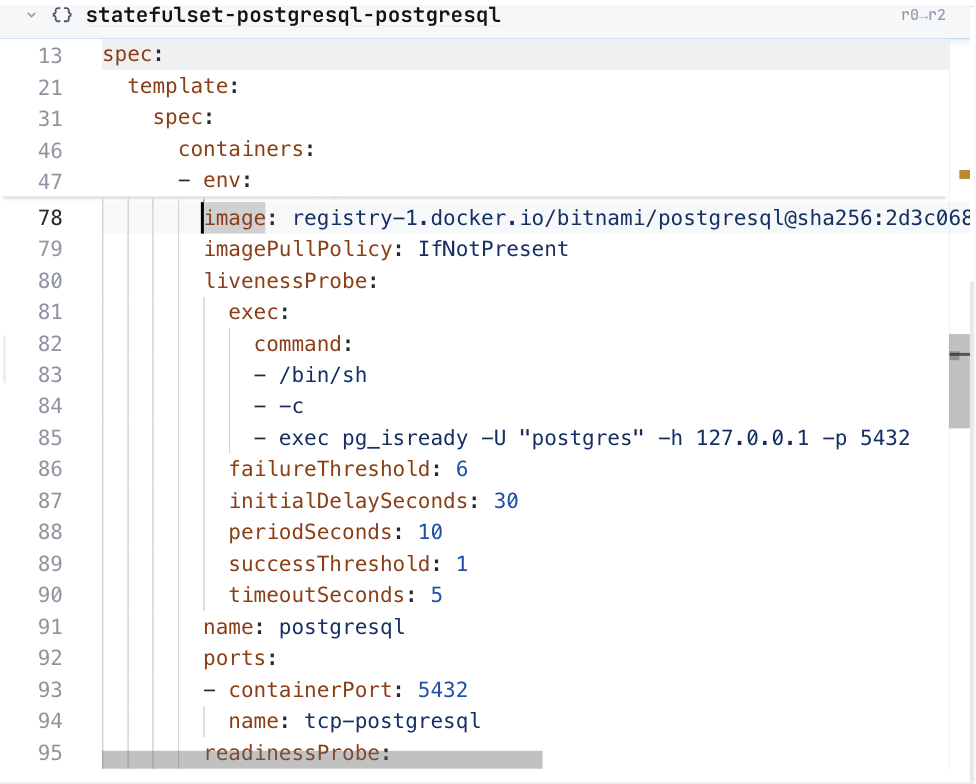
The same image line in ConfigHub, as a plain value. Taken in the helm-catalog organization on 2026-10-25, showing the PostgreSQL StatefulSet, at its image line.
ConfigHub holds this as 8 Units, one for each of the 7 objects the installer writes and one installer record.
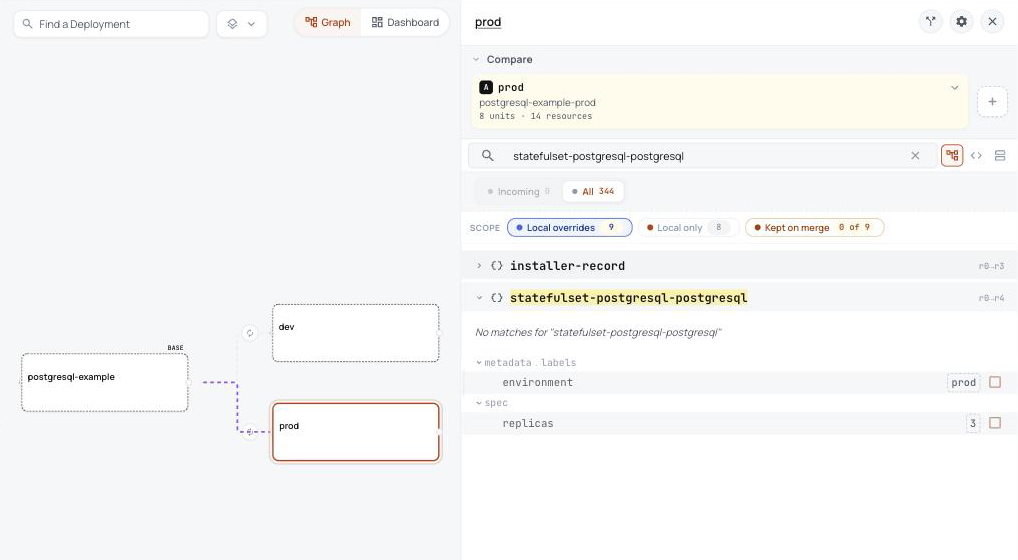
Prod's panel lists what prod changes from the base, here its label and three replicas of its StatefulSet. Taken in the helm-catalog organization on 2026-10-26, showing the PostgreSQL base with its dev and prod variants, and the label and three replicas prod sets on its StatefulSet.
- The template's image line becomes one plain value you can read, and so does every other field.
- Your password stays put. The Helm chart makes a new one every time it runs, and here you create it once.
- The image is pinned to exact bytes, so it can't change under you.
What Helm does that you never see, and what happens here instead
| What Helm does | What happens here instead |
|---|---|
| Makes up a new administrator password every time it renders, so no two renders match. | You create the Secret postgresql/postgresql-auth once, and the chart reads the password from it. |
ConfigHub keeps configuration as plain objects, with a history of every change. Loading puts this chart's objects in a Space, a folder in your ConfigHub organization.
Show me the details (for experienced users)