Before and after
      dnsConfig: {{- include "common.tplvalues.render" (dict "value" .Values.replica.dnsConfig "context" $) | nindent 8 }}
      {{- end }}
      enableServiceLinks: {{ .Values.replica.enableServiceLinks }}
      terminationGracePeriodSeconds: {{ .Values.replica.terminationGracePeriodSeconds }}
      containers:
        - name: redis
          image: {{ template "redis.image" . }}
          imagePullPolicy: {{ .Values.image.pullPolicy | quote }}
          {{- if not .Values.diagnosticMode.enabled }}
          {{- if .Values.replica.lifecycleHooks }}
          lifecycle: {{- include "common.tplvalues.render" (dict "value" .Values.replica.lifecycleHooks "context" $) | nindent 12 }}
          {{- end }}
          {{- end }}
          {{- if .Values.replica.containerSecurityContext.enabled }}
          securityContext: {{- include "common.compatibility.renderSecurityContext" (dict "secContext" .Values.replica.containerSecurityContext "context" $) | nindent 12 }}
          {{- end }}
16 lines of templates/replicas/application.yaml, around its image line. The chart has many files like this.
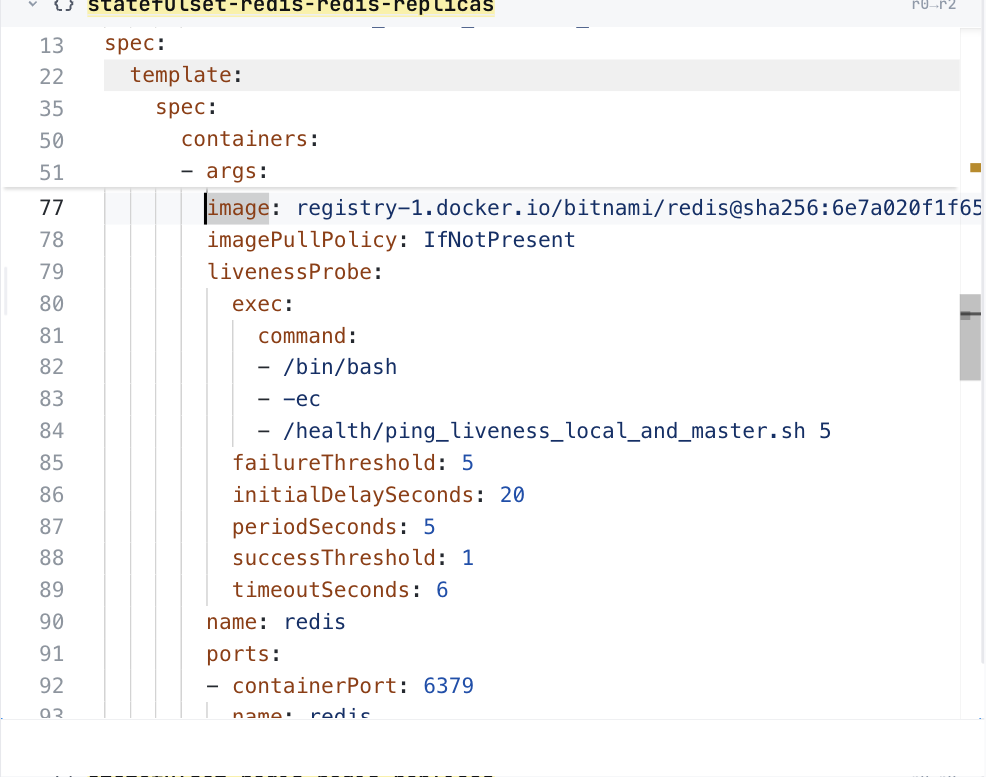
The same image line in ConfigHub, as a plain value. Taken in the helm-catalog organization on 2026-10-25, showing the redis-replicas StatefulSet, at its image line.
ConfigHub holds this as 15 Units, one for each of the 14 objects the installer writes and one installer record.
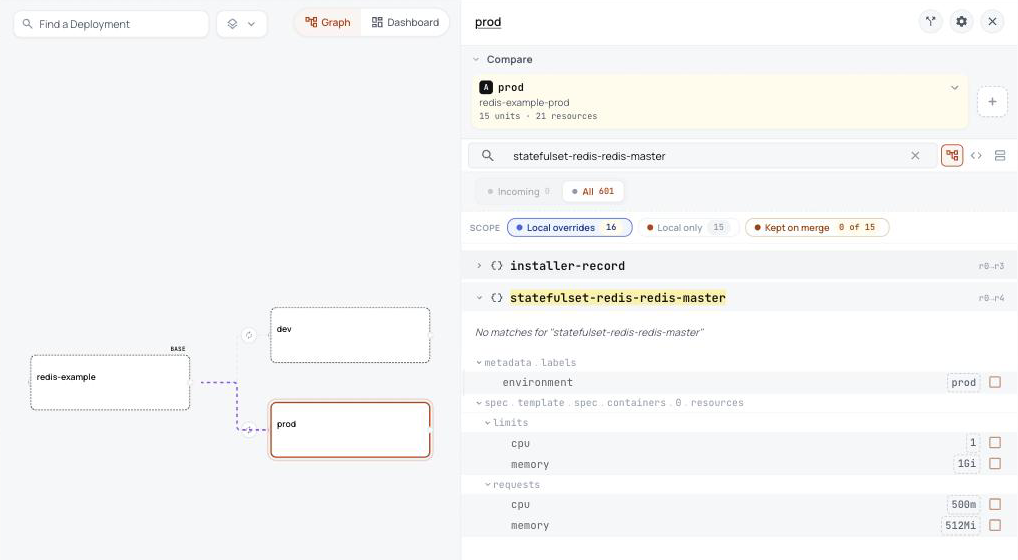
Prod's panel lists what prod changes from the base, here its label and the master's requests and limits. Taken in the helm-catalog organization on 2026-10-26, showing the Redis base with its dev and prod variants, and the label, requests and limits prod sets on the Redis master.
- The template's image line becomes one plain value you can read, and so does every other field.
- Your password stays put. The Helm chart makes a new one every time it runs, and here you create it once.
- The image is pinned to exact bytes, so it can't change under you.
What Helm does that you never see, and what happens here instead
| What Helm does | What happens here instead |
|---|---|
| Makes up a new Redis password every time it renders, so no two renders match. | You create the Secret redis/redis-existing-secret once, and the chart reads the password from it. |
ConfigHub keeps configuration as plain objects, with a history of every change. Loading puts this chart's objects in a Space, a folder in your ConfigHub organization.
Show me the details (for experienced users)